Panic sells. Precision does not.
Whenever a terminal flickers or a diesel generator stutters in Eastern Europe, the digital commentariat rushes to map the incident directly to a clandestine Kremlin operation. A fire breaks out near a transport hub handling satellite ground gear in Poland, and within minutes, breathless headlines attribute the smoke to Russian sabotage. It makes for compelling theater. It feeds the narrative of an omnipotent cyber and kinetic shadow war stretching deep into NATO territory.
It is also an analytical lazy tax.
I have spent years auditing resilient communications architecture in contested environments, and I can tell you right now that the most dangerous enemy of redundant satellite networks is rarely a Spetsnaz operative with a match. It is hardware fatigue, thermal overload, cheap fuel, and maintenance neglect under extreme deployment pressure. When you cram hundreds of high-draw phased-array terminals and commercial power units into makeshift logistics nodes without proper grounding or ventilation, you do not need foreign agents to start a fire. Physics will do it for you.
Let us dismantle the prevailing panic. The reflex to blame targeted sabotage every time a power system chars out in a transit corridor ignores the brutal mechanical realities of field-deployed hardware running past its threshold limits.
The Myth of the Invincible Consumer Dish
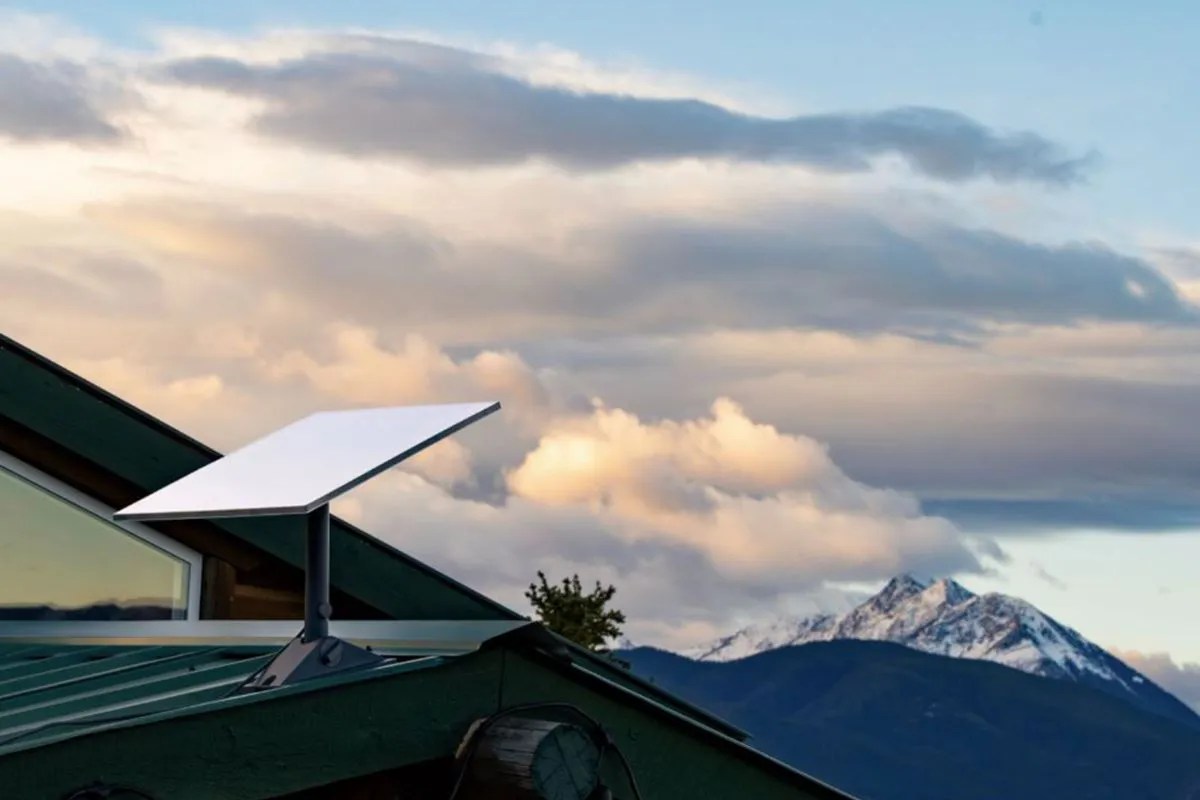
To understand why ground hardware fails, we have to look past the marketing hype of low-Earth orbit constellations. We treat these terminals like consumer routers that happen to point at the sky. They are not. They are power-hungry, high-frequency radio transmitters gulping watts to maintain a lock on constellations moving at thousands of kilometers per hour.
When you deploy consumer-grade hardware into military or frontline logistics zones, you immediately violate every engineering assumption the original manufacturer made. These units are designed for suburban roofs or back-of-truck recreational use, not continuous, maximum-draw operation in dusty, poorly ventilated warehouses subjected to erratic municipal power grids.
Generators fail because tactical supply chains are messy. Fuel quality fluctuates. Maintenance schedules slip because the operators have more pressing priorities than changing oil filters on a backup generator. When a generator surges, it sends a spike straight into the delicate rectifiers and power supplies of attached communications gear. Add a winter load spike, continuous high-throughput data demands, and zero climate control, and you have a recipe for thermal runaway.
A melted generator housing and charred power cables look like a sabotage site only if you want them to. To an engineer, they look like textbook electrical failure caused by overloading.
The Fragility of Centralized Logistics Hubs
The real vulnerability exposed by these incidents is not our susceptibility to covert infiltration, but our dangerous addiction to centralized choke points.
When organizations funnel massive amounts of critical data through single logistical warehouses in transit countries like Poland, they create high-value targets—not just for kinetic attack, but for systemic failure. If you concentrate hundreds of terminals, massive fuel reserves, and heavy power conversion units in one location to streamline shipping, a single localized accident becomes a regional headline.
This is the exact opposite of resilient design. Decentralization is supposed to be the entire point of distributed satellite networks. If a constellation relies on thousands of independent user terminals, why are we routing them through massive, fragile logistics funnels where a single electrical short can disrupt regional throughput?
The strategic failure here is architectural, not tactical. We built a decentralized network in space and anchored it to fragile, highly centralized nineteenth-century industrial logistics on the ground.
Engineering Real Resilience
If we want to survive electronic and kinetic friction, we have to stop treating infrastructure as plug-and-play. True operational security requires shifting away from massive logistics nodes toward hardened, independent micro-deployments.
That means enforcing strict power conditioning on every single terminal deployment. It means abandoning the fantasy that commercial off-the-shelf hardware can run indefinitely in hostile environments without active thermal management and clean power regulation. If a ground station cannot survive a dirty power surge from a failing local generator, it is a liability, not an asset.
Stop looking for shadows in every burnt transformer. Start demanding better engineering, disciplined maintenance, and realistic hardware expectations.
The next fire will not start because of an enemy operative. It will start because we refused to respect the limits of the hardware we are relying on.